
What happened with the use of AI in the evaluation of public sector employees?
On November 4, Homo Digitalis took two complementary actions before the Hellenic Data Protection Authority (HDPA) regarding the use of Artificial Intelligence by the Ministry of the Interior in the evaluation of public sector employees.
1st intervention: We are representing a public sector employee in a complaint filed with the HDPA, requesting an investigation into how the Ministry responded to her request for access to her personal data, as well as broader issues concerning compliance with the General Data Protection Regulation (GDPR).
2nd intervention: We are calling on the HDPA to investigate the matter on its own initiative, as the use of AI may affect thousands of public sector employees who may not have been adequately informed.
We recall that, as early as July 2026, together with the Institute for Research on Regulatory Policies and the public sector employee concerned, we had also filed a complaint with the National Transparency Authority, requesting an investigation into compliance with transparency obligations and the requirements for an algorithmic impact assessment. The complaint is currently under investigation.
Artificial Intelligence in the public sector must not operate without transparency, accountability, and respect for workers’ rights! We will continue to call for meaningful oversight and the protection of everyone’s personal data.

Following a complaint we filed, the Hellenic Data Protection Authority (HDPA) has launched an investigation into the National Intelligence Service
The Hellenic Data Protection Authority launches an investigation into the National Intelligence Service (EYP), following a complaint filed by us!
As early as 1997, data protection legislation did not exempt the National Intelligence Service (EYP) from the Authority’s supervisory oversight. Furthermore, the EYP’s internal regulations have required the Service to comply with personal data protection legislation since 2008. However, in 2019, the Mitsotakis government, through Law 4624/2019, restricted the Authority’s competence to oversee the processing of classified personal data by the EYP.
In November 2022, the HDPA itself, in an opinion submitted to the Ministry of Justice, highlighted serious concerns regarding the constitutionality of the legal framework and the effective protection of personal data processed by the EYP. The Authority’s recommendations were not incorporated into the revision of the legislative framework in December 2022 by the then Minister of Justice, Konstantinos Tsiaras.
In March 2026, a citizen represented by our organisation attempted to exercise their personal data protection rights before the EYP by submitting an access request, invoking specific provisions of the law. The EYP failed to respond to the request. As a result, in June 2026, we filed a formal complaint with the Authority.
In October, we were informed that the Authority had launched an investigation into our complaint, requesting that the EYP respond to specific questions concerning its failure to address the citizen’s access request. This is an important development in our efforts to clarify the EYP’s obligations and establish the extent to which the processing of personal data by the Service is subject to independent oversight.
The crucial question remains: How can the protection of personal data be guaranteed in practice when such data is in the hands of the National Intelligence Service?
National security and the protection of fundamental rights must go hand in hand, supported by clear rules, meaningful safeguards, and effective oversight.
Palantir Has No Place Here!
Palantir Has No Place Here!
Together with 127 organisations and trade unions from across Europe, we are calling on governments and the European Commission to cancel their public contracts with Palantir. We would like to thank journalist Dimitris Elafropoulos, who highlighted our joint letter in an article published in the newspaper TO VIMA and featured comments from our Executive Director, Eleftherios Chelioudakis.
Palantir is an American technology company that develops software for surveillance, law enforcement, healthcare data processing, and military operations.
In Greece, the company collaborated with the Ministry of Digital Governance in 2020, during the COVID-19 pandemic. At the time, together with Inside Story and Vouliwatch, we brought the related concerns to public attention. Homo Digitalis also requested an investigation by the Hellenic Data Protection Authority (HDPA), which subsequently led to Decision 43/2022.
Read our joint letter here.
Read Dimitris Elafropoulos’s article in the newspaper TO VIMA here.
The Government’s Third Bill on Social Media Use by Minors
The Government’s approach remains practically unenforceable and, moreover, is now moving in a direction that runs counter to the European Commission’s proposal.
More specifically, following the first bill in April and the second in July 2026, the Government is now introducing a third bill which, instead of providing solutions, creates new problems. The bill was submitted to Parliament on October 13, with its adoption scheduled for October 22.
Despite repeated government announcements, the bill does not require platforms to use KidsWallet or Gov.gr Wallet for age verification. Their use remains optional. In simple terms, this is a regulation without any meaningful enforcement mechanism. Yet another publicity stunt!
At the same time, the Greek approach also runs counter to the European Commission’s proposed EU Kids Act, which covers not only social media, but also video-sharing platforms and video games.
All this is happening despite the legal analyses, letters, and public interventions we have made over the past few months, highlighting specific challenges concerning children’s digital rights and the protection of the digital commons.
The Government has shown no genuine interest in engaging with these concerns. We were not even invited to appear before the competent Parliamentary Committee, despite being nominated by opposition parties. Protecting children online cannot be achieved through publicity stunts.
11 Civil Society Organizations Submit Joint Recommendations on the Implementation of the AI Act in Greece
Following their participation in the public consultation launched by the Hellenic Ministry of Digital Governance and Artificial Intelligence on the draft law implementing the AI Act in Greece, 11 civil society organizations have submitted a joint letter to the Special Secretariat for Artificial Intelligence & Data Governance, setting out their recommendations for improving the draft legislation.
Among other issues, the organizations highlight the need to substantially strengthen the Hellenic Data Protection Authority, so that it can effectively fulfill the critical supervisory role assigned to it. Similar concerns have also been raised by the Authority itself in its recent Opinion on the draft law.
Furthermore, making use of the discretion granted to Member States under the European Regulation, we call on Greece to introduce a complete ban on real-time remote biometric identification for law enforcement purposes. The exceptions provided for under the Regulation pose serious risks to fundamental rights and could lead to disproportionate surveillance practices.
We propose a similar approach to the use of comparable technologies for post-event identification, which is currently classified as a high-risk application.
You can read the joint letter at the link below, as well as on the public consultation webpage: https://lnkd.in/dTgjXE4M
The 11 organizations in alphabetical order:
-Network For Children’s Rights
– Greek Forum of Migrants
– Hellenic Informatics Union
– INERP – Institute for Regulatory Policy Research
-Diotima Centre
-HIAS Greece
-Homo Digitalis
-I Have Rights.
-Ιn contACT
-Open Lab Athens
-Visible Machines (VM)
Homo Digitalis Submits an Access to Documents Request to the European Commission Regarding the AI Act
The AI Act was revised. But who shaped the evidence behind that decision? On 29 June, the EU gave its final green light to the Digital Omnibus AI package, revising parts of the AI Act before many of its obligations had even entered into force.
The European Commission additionally relied on an AI Pact survey to support claims that compliance costs were too high. But we wanted to know:
-Who responded to that survey?
-Was the evidence representative of the broader AI ecosystem?
To find out, Homo Digitalis submitted an access-to-documents request to the European Commission, DG CONNECT. They refused to disclose the identities of the respondents, but our request still revealed something important:
Only 44 out of more than 230 AI Pact companies participated in the survey.
Nearly half of those respondents were companies with more than 750 employees.
We also asked for an anonymous breakdown by company size, sector, and geography so that the public could better assess the survey’s representativeness. That information was not meaningfully provided.
When survey evidence is used to justify changes to EU law, citizens should be able to scrutinize whether that evidence is representative, robust, and worthy of informing public policy. That’s why we have now submitted a confirmatory application, asking the European Commission to review its decision.
Read our FOIA and the documents shared by the European Commission here: https://lnkd.in/dyRuAu8S
Our joint statement on the Draft Law “Implementation of the Pact on Migration and Asylum” regarding the use of AI in asylum procedures
Together with the organisations I Have Rights, Network for Children’s Rights, WHEN.org.gr, Open Lab Athens, Greek Forum of Migrants and HIAS Greece, we published a joint statement expressing our observations on the Draft Law “Implementation of the Pact on Migration and Asylum” regarding the use of Artificial Intelligence in asylum procedures.
The Draft Law was open for public consultation until 25/5, introducing a new framework for screening procedures, international protection procedures, the operation of Eurodac, and the management of biometric and other personal data of asylum seekers and migrants. It explicitly provides for the possibility of using artificial intelligence systems in the processes of information provision, interpretation, translation, and the recording of personal interviews of applicants for international protection.
These provisions raise significant challenges regarding data protection, transparency, non-discrimination, and effective judicial protection, particularly in light of the General Data Protection Regulation (GDPR), the Charter of Fundamental Rights of the European Union, and the Artificial Intelligence Act (AI Act).
You can read our joint statement here!
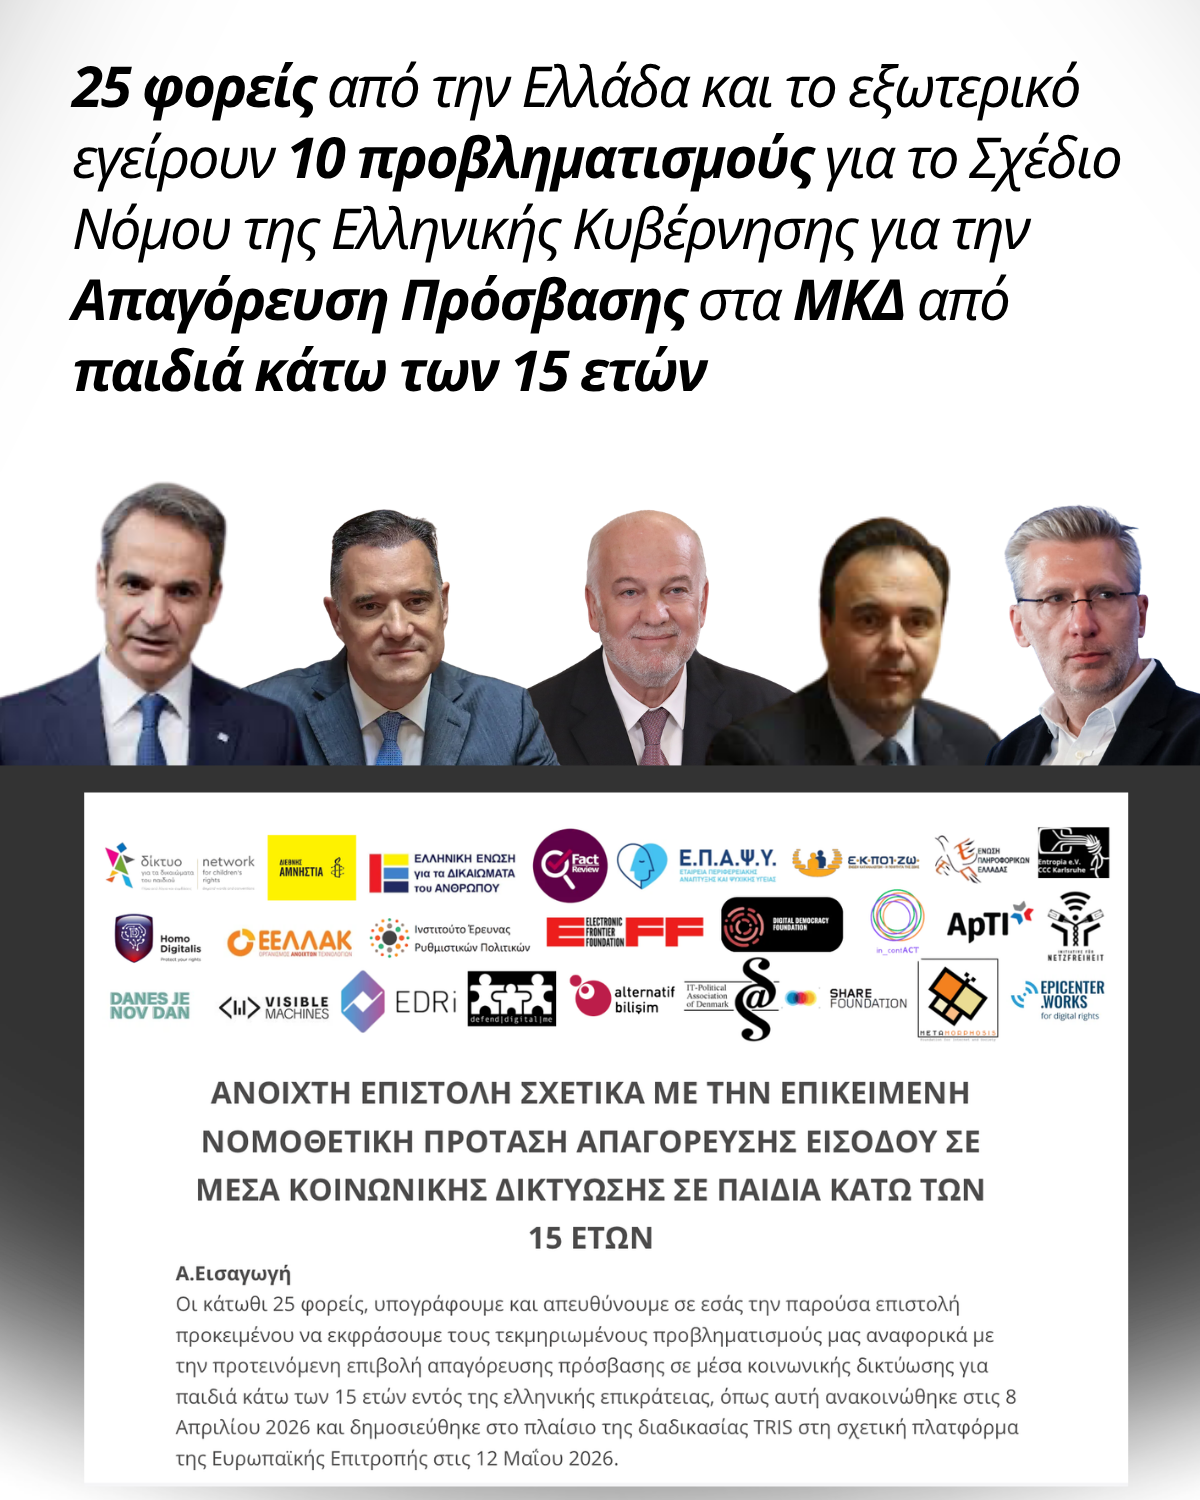
25 Greek and international organizations raise concerns to the Prime Minister and the competent Ministers regarding the Draft Law on the Prohibition of Access to Social Media for Children under 15 years old.
Since early April, when the government announced in a press conference its intention to ban minors under the age of 15 from accessing social media platforms, the issue has become the focus of intense public debate. Parents, educators, scientists, youth organizations, and technology experts have all presented arguments concerning the boundaries between protection, control, and digital freedom.
In the early hours of Tuesday, May 12, this discussion took on an official legislative dimension. The Draft Law on the Prohibition of Access to Social Media for Children Under 15 was uploaded to the European Commission’s TRIS platform, initiating the notification and international consultation process.
Just one week later, the reaction became collective. Twenty-five (25)* Greek and international organizations active in mental health, child protection, combating disinformation, digital rights, consumer protection, computer science, human rights, open technologies, and the institutional functioning of the rule of law joined their voices in a joint letter addressed to Prime Minister Kyriakos Mitsotakis and the relevant ministers.
The organizations’ intervention does not merely express general disagreement with the proposed measure. Rather, it presents an extensive and multi-layered 19-page critique addressing issues ranging from privacy and cybersecurity to compatibility with European law, the principles of participatory and evidence-based legislation, and the fundamental rights of children.
The Measure’s Scope Would Affect All Users, Regardless of Age
In their joint letter, the signatories warn that the planned “re-verification of age” would not apply only to minors, but effectively to all internet users in Greece, turning identification and surveillance into prerequisites for access to the digital public sphere. They argue that the mandatory use of age-verification tools and digital wallets could gradually erode online anonymity and fundamentally alter the nature of the internet itself by establishing “digital gateways” for every online service.
Lack of Transparency, Consultation, and Evidence
Particular criticism is also directed at the way the legislative initiative was advanced. The organizations refer to a lack of participatory procedures and the absence of meaningful consultation with scientists, institutions, civil society organizations, and even children themselves. At the same time, they express serious concern that, according to allegations, the recommendation of the competent committee of KESY, which reportedly viewed generalized bans with caution, was neither published nor apparently taken into account before the government’s announcements.
At the core of the criticism lies the proportionality of the measure. While the authors acknowledge the real risks associated with minors’ use of social media, they argue that instead of blanket restrictions, policies should invest in digital literacy, the education of children and parents, and the redesign of platforms themselves to limit addictive and exploitative mechanisms.
Socioeconomic Exclusion
The organizations also express fears that the measure could lead to social exclusion, affecting families lacking sufficient digital skills or access to modern devices. They further warn that minors may turn to unregulated platforms or circumvention techniques such as VPNs, ultimately exposing their personal data to even greater risks.
Communication Ambiguities and Legal Challenges
In even sharper terms, the organizations criticize the government’s public presentation of the regulation, referring to contradictory statements, ambiguities, and communication strategies that, they argue, obscure rather than clarify the true scope of the measure.
The authors note that while the Ministry of Health described the proposal as a “clear and coherent framework fully aligned with European law,” the same announcement admitted that further examination would be required to determine whether the measure could ultimately be implemented without legal conflicts with the European framework. According to the organizations, this contradiction is not merely a communication misstep but an indication of deeper legal uncertainty that could even lead to referrals to the Court of Justice of the European Union, delaying or weakening implementation.
The actual scope of the ban is also placed under scrutiny. As noted, the legislative initiative would not concern only large commercial platforms such as TikTok, Instagram, or Facebook, but, based on the definition contained in the European DMA Regulation, could extend horizontally to any “online social networking service,” including decentralized platforms of the so-called Fediverse such as Mastodon and PixelFed. The organizations emphasize that these platforms operate according to an entirely different philosophy, without centralized corporate control or algorithmic mechanisms that encourage user addiction, making their inclusion under the same regulatory framework problematic.
At the same time, the organizations question why video-sharing platforms such as YouTube are excluded from the regulation, despite being a core part of children’s daily digital lives and featuring similarly addictive content. According to the text, this distinction has not yet been adequately justified by the government, nor is it accompanied by quantitative or scientific data explaining the differentiation.
The legal argument concerning compatibility with European law is also extensive. The organizations argue that Greece risks introducing additional national obligations in an area already centrally regulated by the Digital Services Act (DSA), thereby violating the principle of uniform application of rules within the European digital market. As they point out, the DSA provides measures for the protection of minors, but not blanket age-based access bans enforced through mandatory identity verification.
The text further warns that imposing such a model could ultimately work against children’s interests by weakening pressure on platforms to make their environments safer and shifting the entire burden of protection onto user identification and exclusion. “The core model of the DSA concerns the management of systemic risks, not the prohibition of specific categories of users,” the letter states.
The organizations conclude that instead of adopting new measures of questionable effectiveness and high legal risk, the Greek state should focus on the effective implementation of the already existing European framework for the protection of minors and personal data—a framework which, they argue, remains insufficiently enforced against major digital platforms.
The joint statement closes with four key demands directed at the government:
- an open and inclusive public consultation process,
- publication of the KESY recommendation,
- full disclosure of the technical and legal opinions accompanying the measure, and
- the adoption of policies obliging platforms themselves to become safer for all users, not only children under 15.
The letter is available in both Greek and English.
The publication of the joint letter took place on Sunday, May 24, in an article by NEWS 247 and journalist Eftychia Soufleri.
The 25 organizations signing the letter are the following (in alphabetical order):
Yours sincerely,
- Asociația pentru Tehnologie și Internet (ApTI)
- Alternatif Bilisim
- Amnesty International – Greek Section
- Chaos Computer Club Karlsruhe – Entropia e.V.
- Danes je nov dan, Inštitut za druga vprašanja
- Defend Digital Me
- Digital Democracy Foundation
- Electronic Frontier Foundation
- EPAPSY (Association for Regional Development and Mental Health)
- epicenter.works – for digital rights
- Electronic Fronter Foundation
- European Digital Rights (EDRi)
- FactReview
- Hellenic Informatics Union (EPE)
- Hellenic League for Human Rights
- Homo Digitalis
- Initiative für Netzfreiheit
- In_contACT org
- IT-Pol Denmark
- Metamorphosis Foundation
- Network for Children's Rights
- Open Technologies Alliance (GFOSS)
- Research Institute for Regulatory Policies
- SHARE Foundation
- Union of Consumers “Quality of Life” (EKPIZO)
- Visible Machines – AI Research and Social Awareness Cent
*The Electronic Frontier Foundation and the Defend Digital Me co-signed the joint letter one day after its submission, as an expression of support for the initiative, specifically on 20 May 2026.
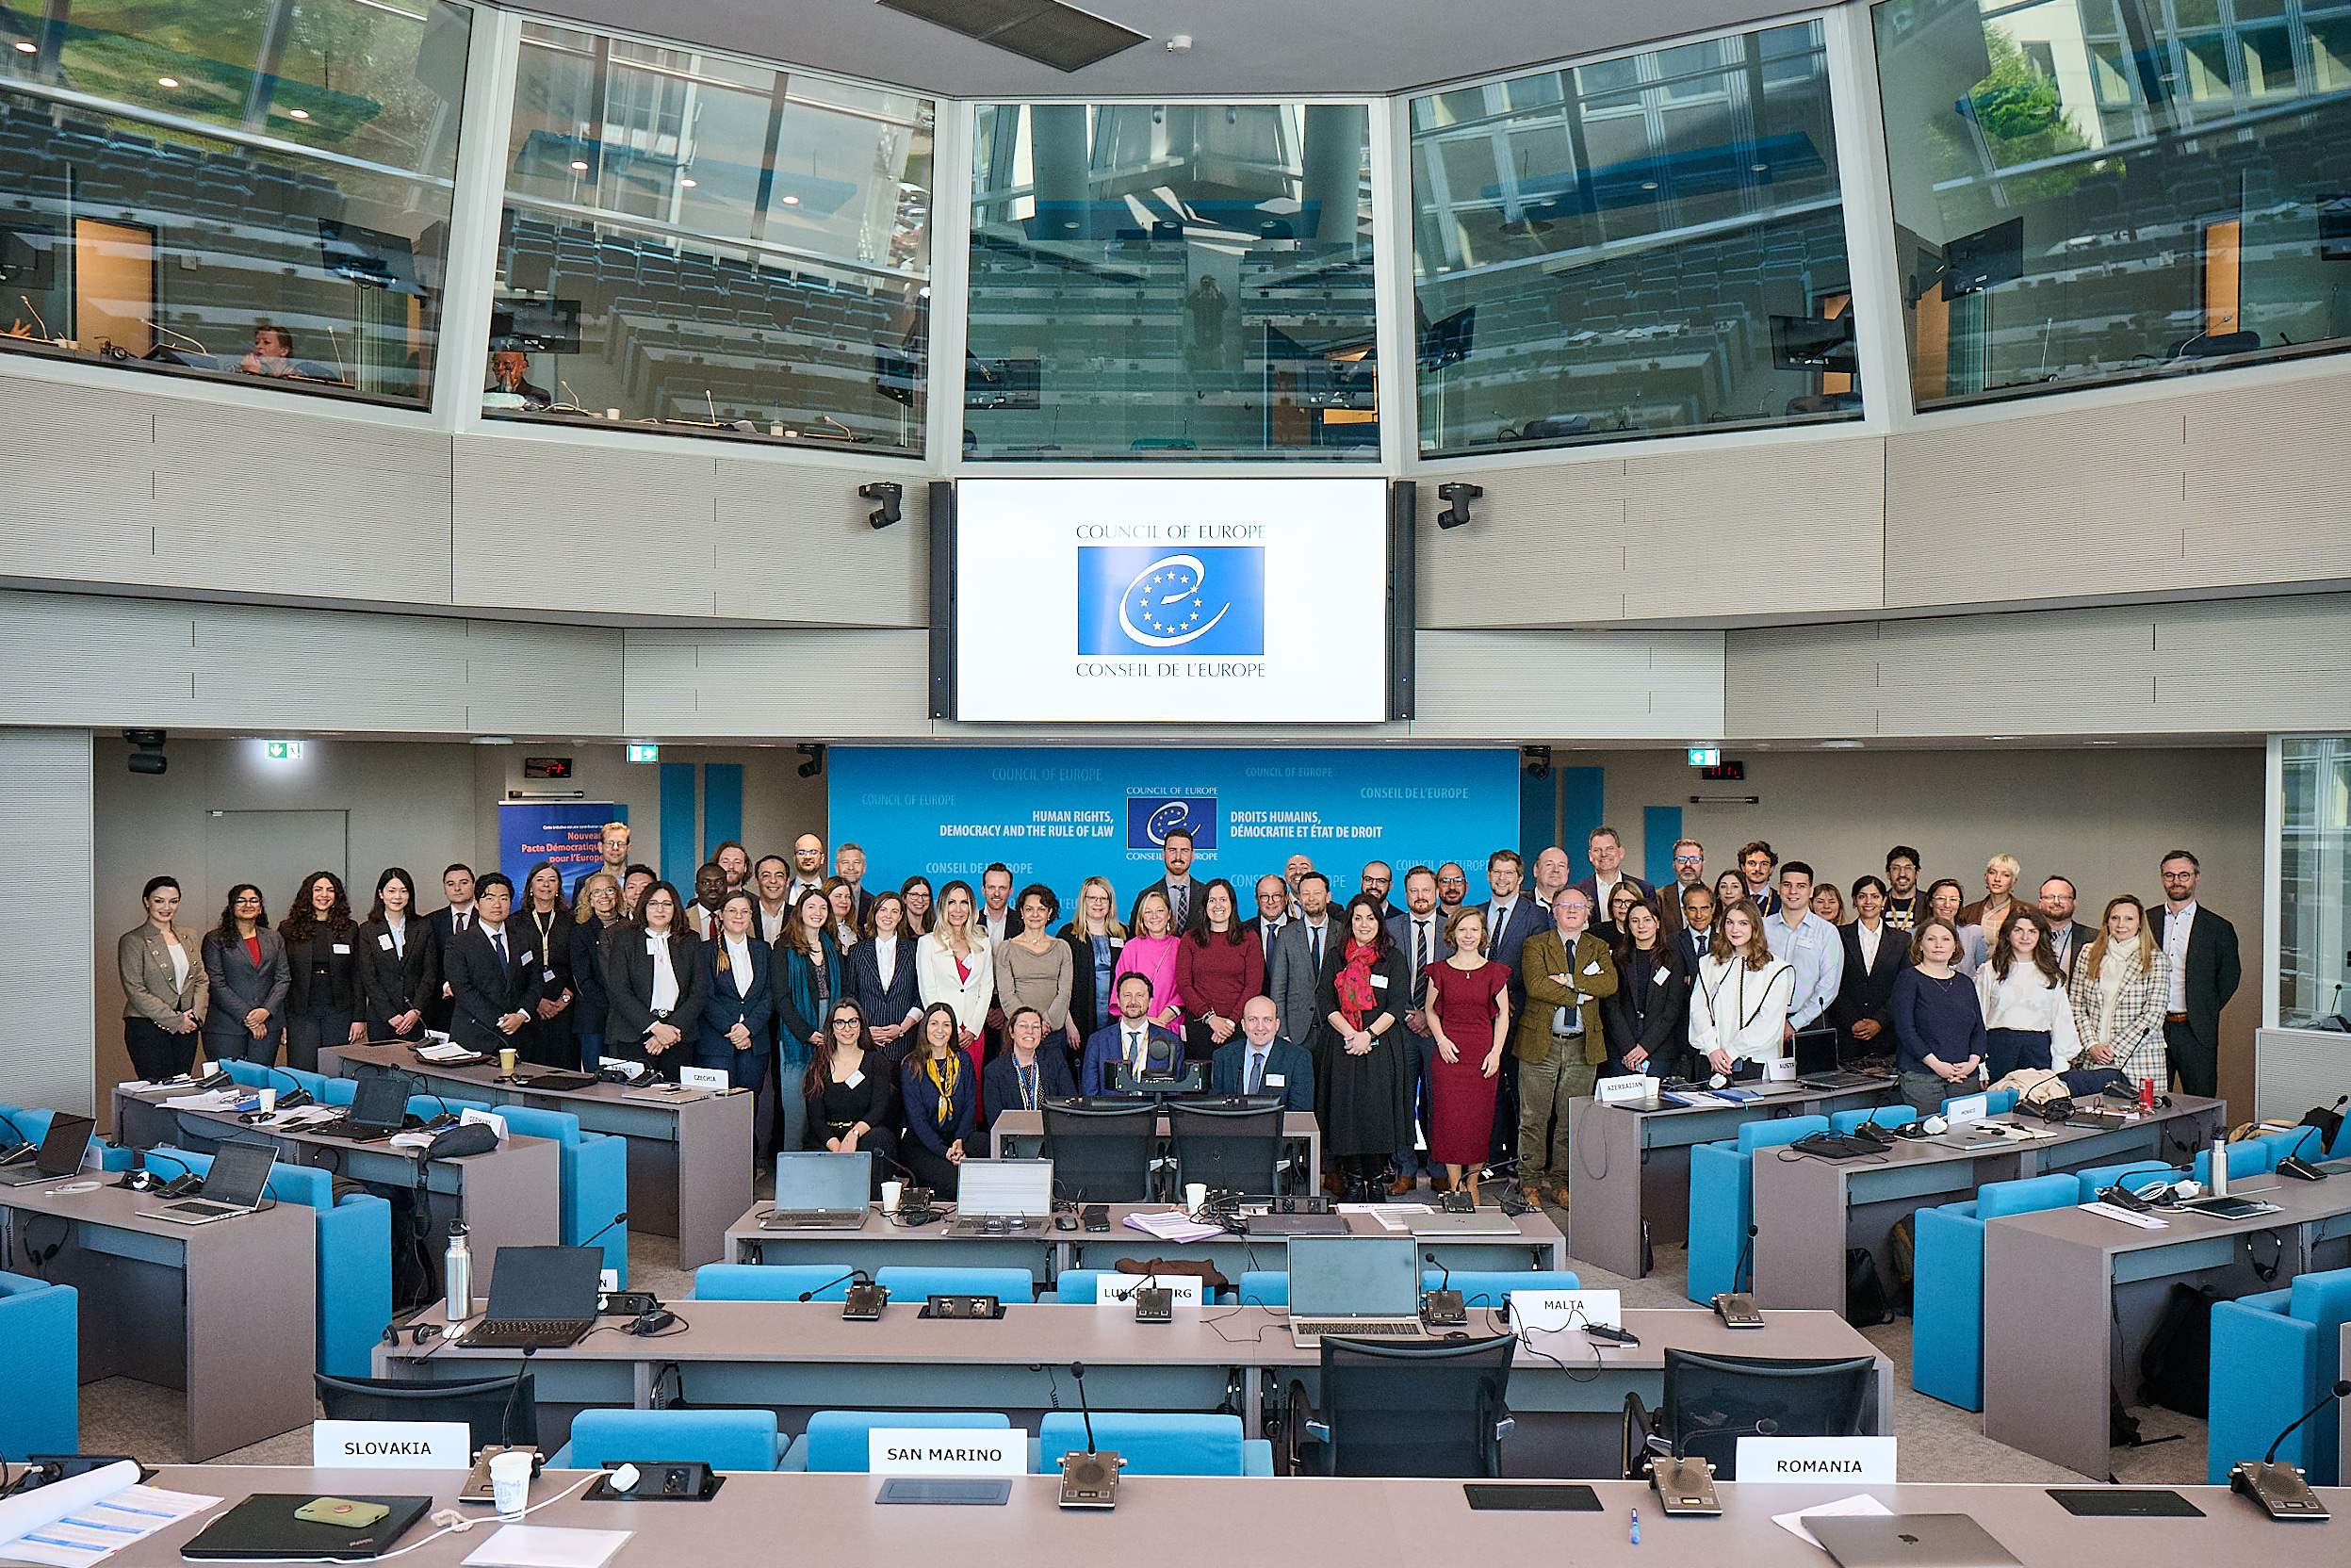
Homo Digitalis is an observer member of the new Council of Europe Committee CDNET
Homo Digitalis is proud to have been admitted as an observer organisation to the Council of Europe’s Steering Committee for New and Emerging Digital Technologies (CDNET)
Building on our previous participation as observers in the Council of Europe’s Ad hoc Committee on Artificial Intelligence (CAHAI) in 2020 and the Committee on Artificial Intelligence (CAI) in 2022, we look forward to strengthening our engagement in this newly established forum and further contributing to meaningful dialogue, collaboration, and policy development on emerging digital technologies.
Read more about CDNET here.